
01
Plan
Know what you're defending
Model the system and map the real attack surface, guided by AI and grounded in your architecture.
AI-powered threat modeling and compliance mapping for teams without the people, time, or in-house expertise. Wherever the gap is, MadThreat fills it. No compromise on rigor.
MadThreat brings AI-powered threat modeling and compliance mapping to the IT admin already wearing five hats, the consultant juggling ten client engagements, the engineering team that never quite finds the runway to do it properly, and the MSP trying to standardize a real process across every account instead of reinventing it each time.
Wherever the gap is, people, time, or expertise, MadThreat fills it. No compromise on rigor.
AI does the initial analysis, so whether you're going at it alone or bringing in a specialist, you're never starting from a blank page.
The same depth of analysis and framework coverage enterprise security tooling promises, priced for teams that don't have an enterprise budget.
For multiple clients, repeatable threat modeling. Same rigor and frameworks, a fraction of the time.
Threat modeling has traditionally required deep security expertise most teams simply don't have in-house, or don't have enough of. MadThreat closes that gap, giving anyone, expert or not, a strong starting point.
Consultants can deliver consistent, framework-mapped work faster, with the same rigor and less manual effort. Seven steps take every team from question to defensible answer.
Each capability below removes hours of work your team is doing by hand today.
Plan-Do-Check-Act is how mature security programs stay current. MadThreat keeps that work connected and moving.
Model the system and map the real attack surface, guided by AI and grounded in your architecture.
Turn recommendations into owned actions with clear effort, budget, priority and completion status.
Review risk position and evidence against STRIDE, MITRE and the frameworks your stakeholders expect.
Keep changes versioned, progress measurable and every report aligned to the same source of truth.
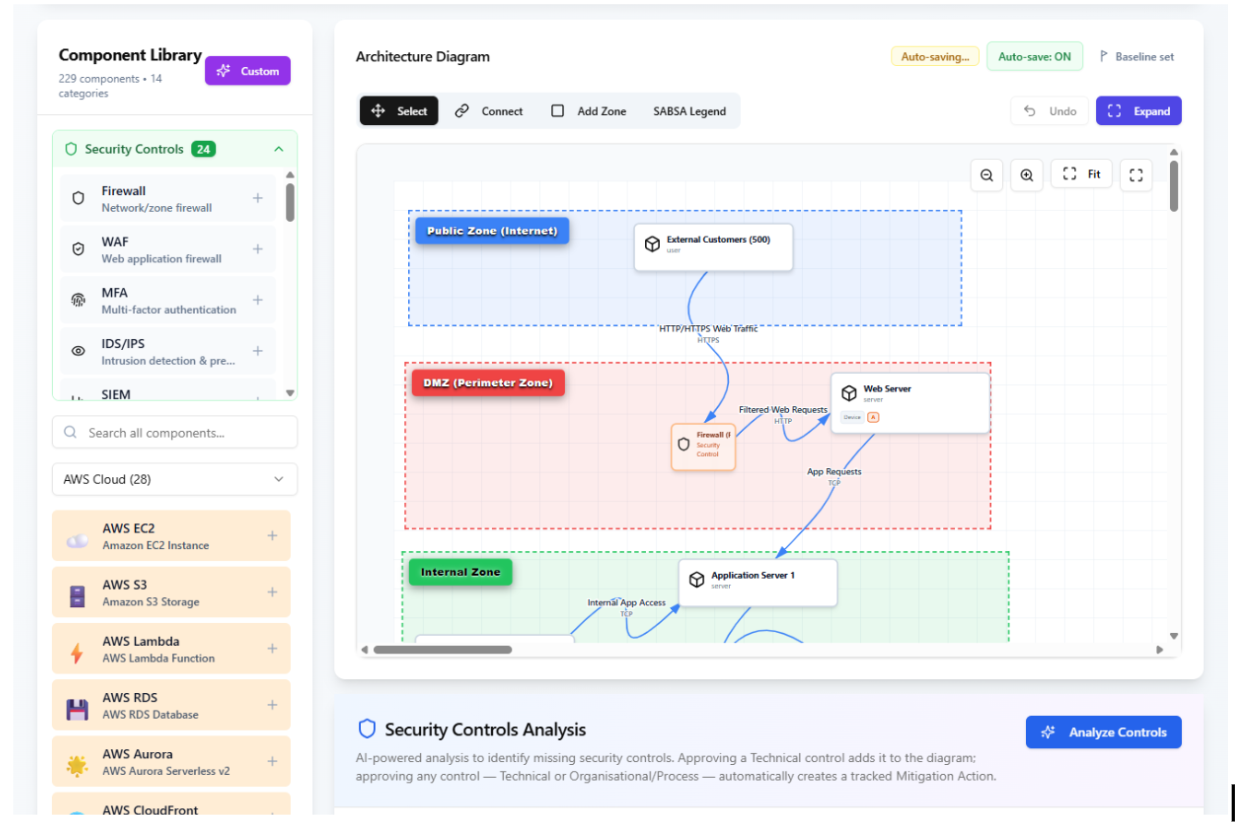
Pick a template or describe the system in your own words. The architecture is editable from the first second.
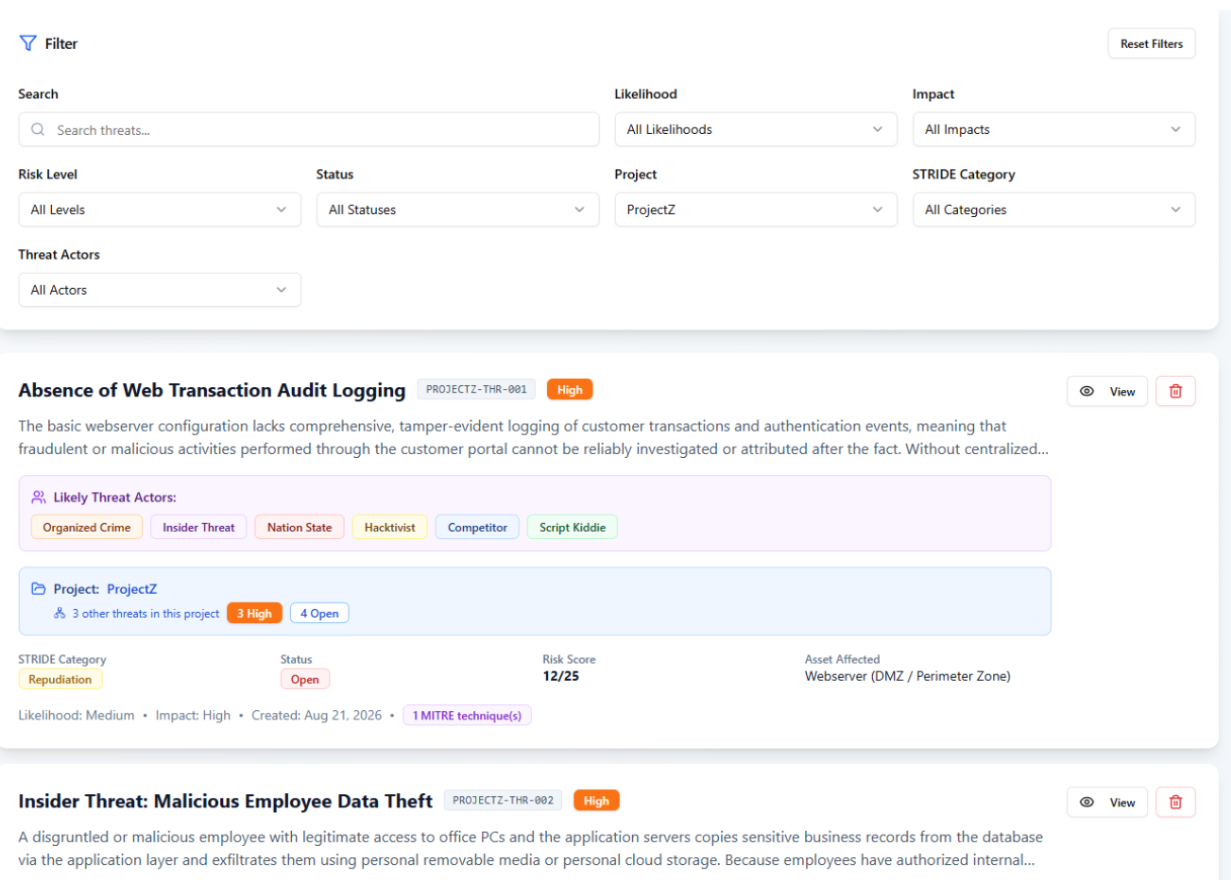
Risks arrive scored by likelihood and impact, mapped to STRIDE and MITRE ATT&CK, with the next mitigation already attached.
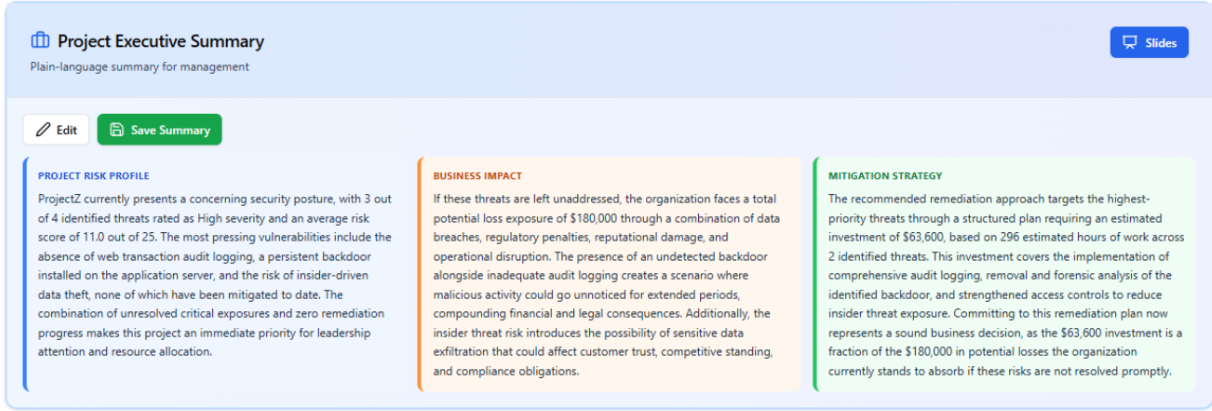
Risk profile, business impact and mitigation strategy in one branded export. Ready in seconds, not the night before the board meeting.
Use cases for teams where security is the whole role, or one responsibility among many.
Responsible for security, but security isn't their only job.
Run a threat model before a new system goes live, catch missing controls before an audit, and keep a living record of fixes without needing a full-time security resource.
Threat modeling matters, but it gets pushed when deadlines hit.
MadThreat helps turn work that can take days into something achievable in an afternoon.
Deliver professional, framework-mapped assessments.
Let AI handle the heavy lifting while you keep control of human judgment and the client relationship.
Standardize threat modeling across every client.
Onboard, threat model, and create a remediation roadmap using a repeatable, consistent process.
Show investors, customers and enterprise prospects that security is being taken seriously.
Create audit-ready findings and a clear compliance story.
Working toward or maintaining NIS2 · ISO 27001 · SOC 2 · GDPR.
Know where you stand and close the gaps.
Straightforward plans for individuals, teams and regulated organizations. 2-day trial
A security platform should be held to the standard it asks of everyone else.
Security is not one control at one boundary. MadThreat uses layers of protection, including database-enforced access controls, strong required authentication, and monitoring at multiple layers. If one layer is tested, others remain.
Strong authentication is required for every account from day one.
Row-level security architecture and database-enforced access controls keep customer data structurally isolated.
Clients, auditors and external stakeholders can review findings without receiving full account access.
Data is encrypted in transit and at rest.
Automated daily backups protect operational continuity.
Meaningful account and administrative actions are logged.
Unusual concurrent login patterns can be flagged.
Structured testing covers the OWASP Top 10 and deeper application-specific risks, including access-control edge cases, data integrity, business logic, and issues automated scanners can miss.
MadThreat gets its name from two ideas.
Mad is a nod to Madrid, the city where the platform was created.
And mad is also about thinking outside the box, questioning the obvious, challenging assumptions, and approaching problems from unexpected angles.
Because threats don't always follow the rules. Why should threat modeling?
That's the idea behind MadThreat: a different way to think about, visualize, and manage cybersecurity threats.
Something we haven't covered? Ask us, and our team will help.
No. AI performs the initial analysis, so you start from a structured threat model rather than a blank page. Specialists get a faster starting point; everyone else gets a defensible one.
Findings are mapped to the frameworks teams are usually held to, including ISO 27001, NIS2, SOC 2 and GDPR, alongside STRIDE and MITRE ATT&CK classification.
Yes. Upgrade, downgrade or cancel at any time. Changes apply immediately and billing is prorated automatically.
Yes, on every plan, at 20% below monthly. Enterprise annual terms are agreed directly with our team.
Whether you want a walkthrough of the platform, have questions about how it fits your setup, or just want to sanity-check an idea, write to us.
support@madthreat.com